
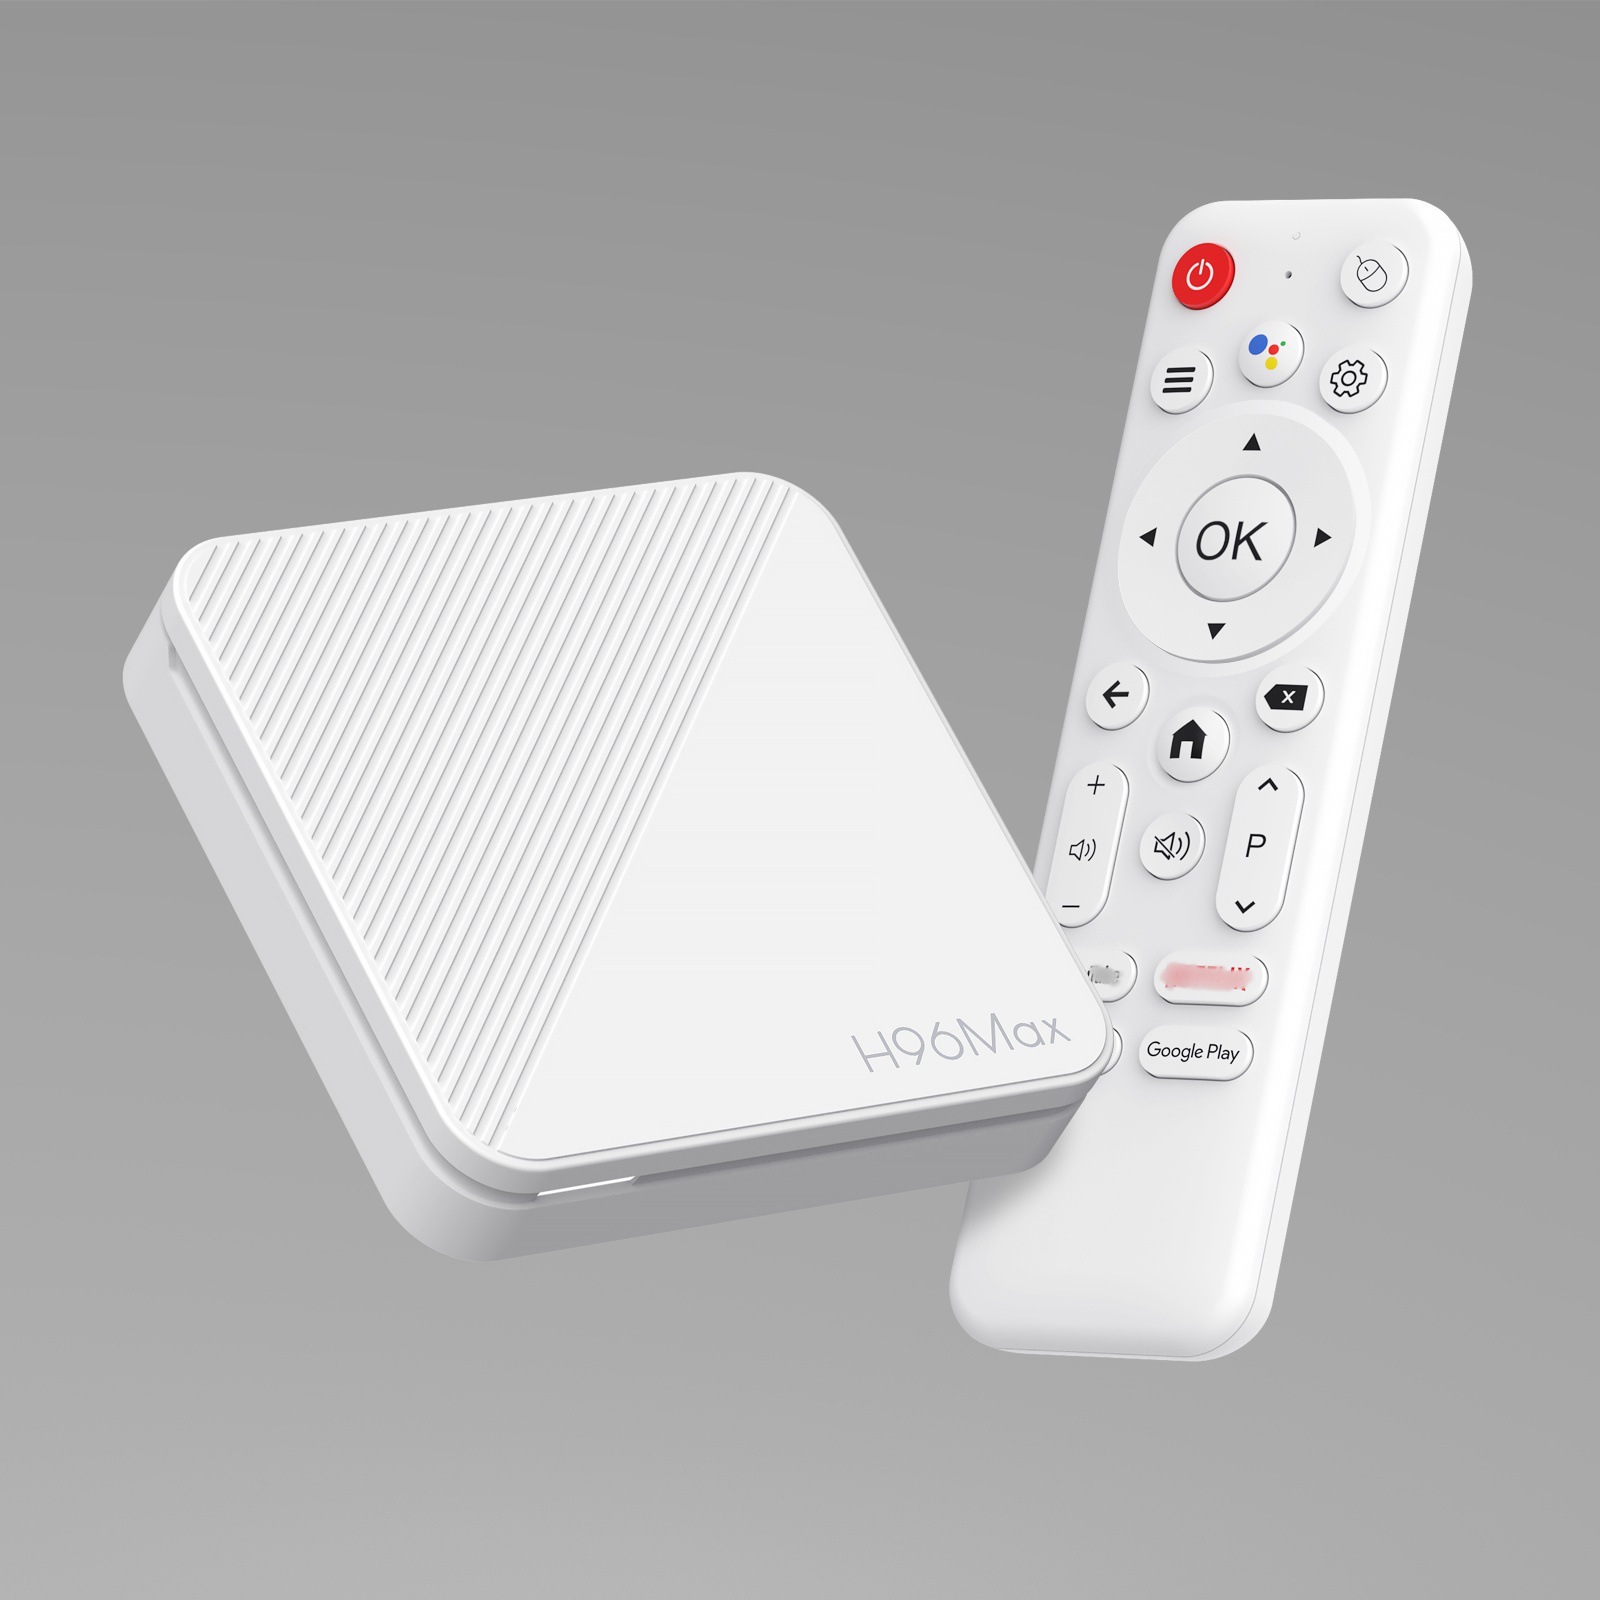
The scale of the operation extended far beyond simple boxes. Investigators found the malware pre-installed across a wide range of Android-based hardware, including telehealth equipment, digital signage, and karaoke machines. By utilizing sophisticated obfuscation techniques, the manufacturer triggered the infection the moment users first booted up their new hardware, keeping the process hidden from owners for years.
Videostrong monetized this access by selling entry points to criminal affiliates who deployed secondary malware modules. These agents funneled traffic through residential proxy networks and siphoned data for financial gain. While Google has dismantled the primary command-and-control infrastructure associated with the manufacturer, the cleanup process is ongoing. By disrupting the broader network domains used by these criminal affiliates, Google estimates it has effectively blocked access to at least 10 million other devices compromised through parallel distribution channels.
Comments (0)
No comments yet. Be the first!