
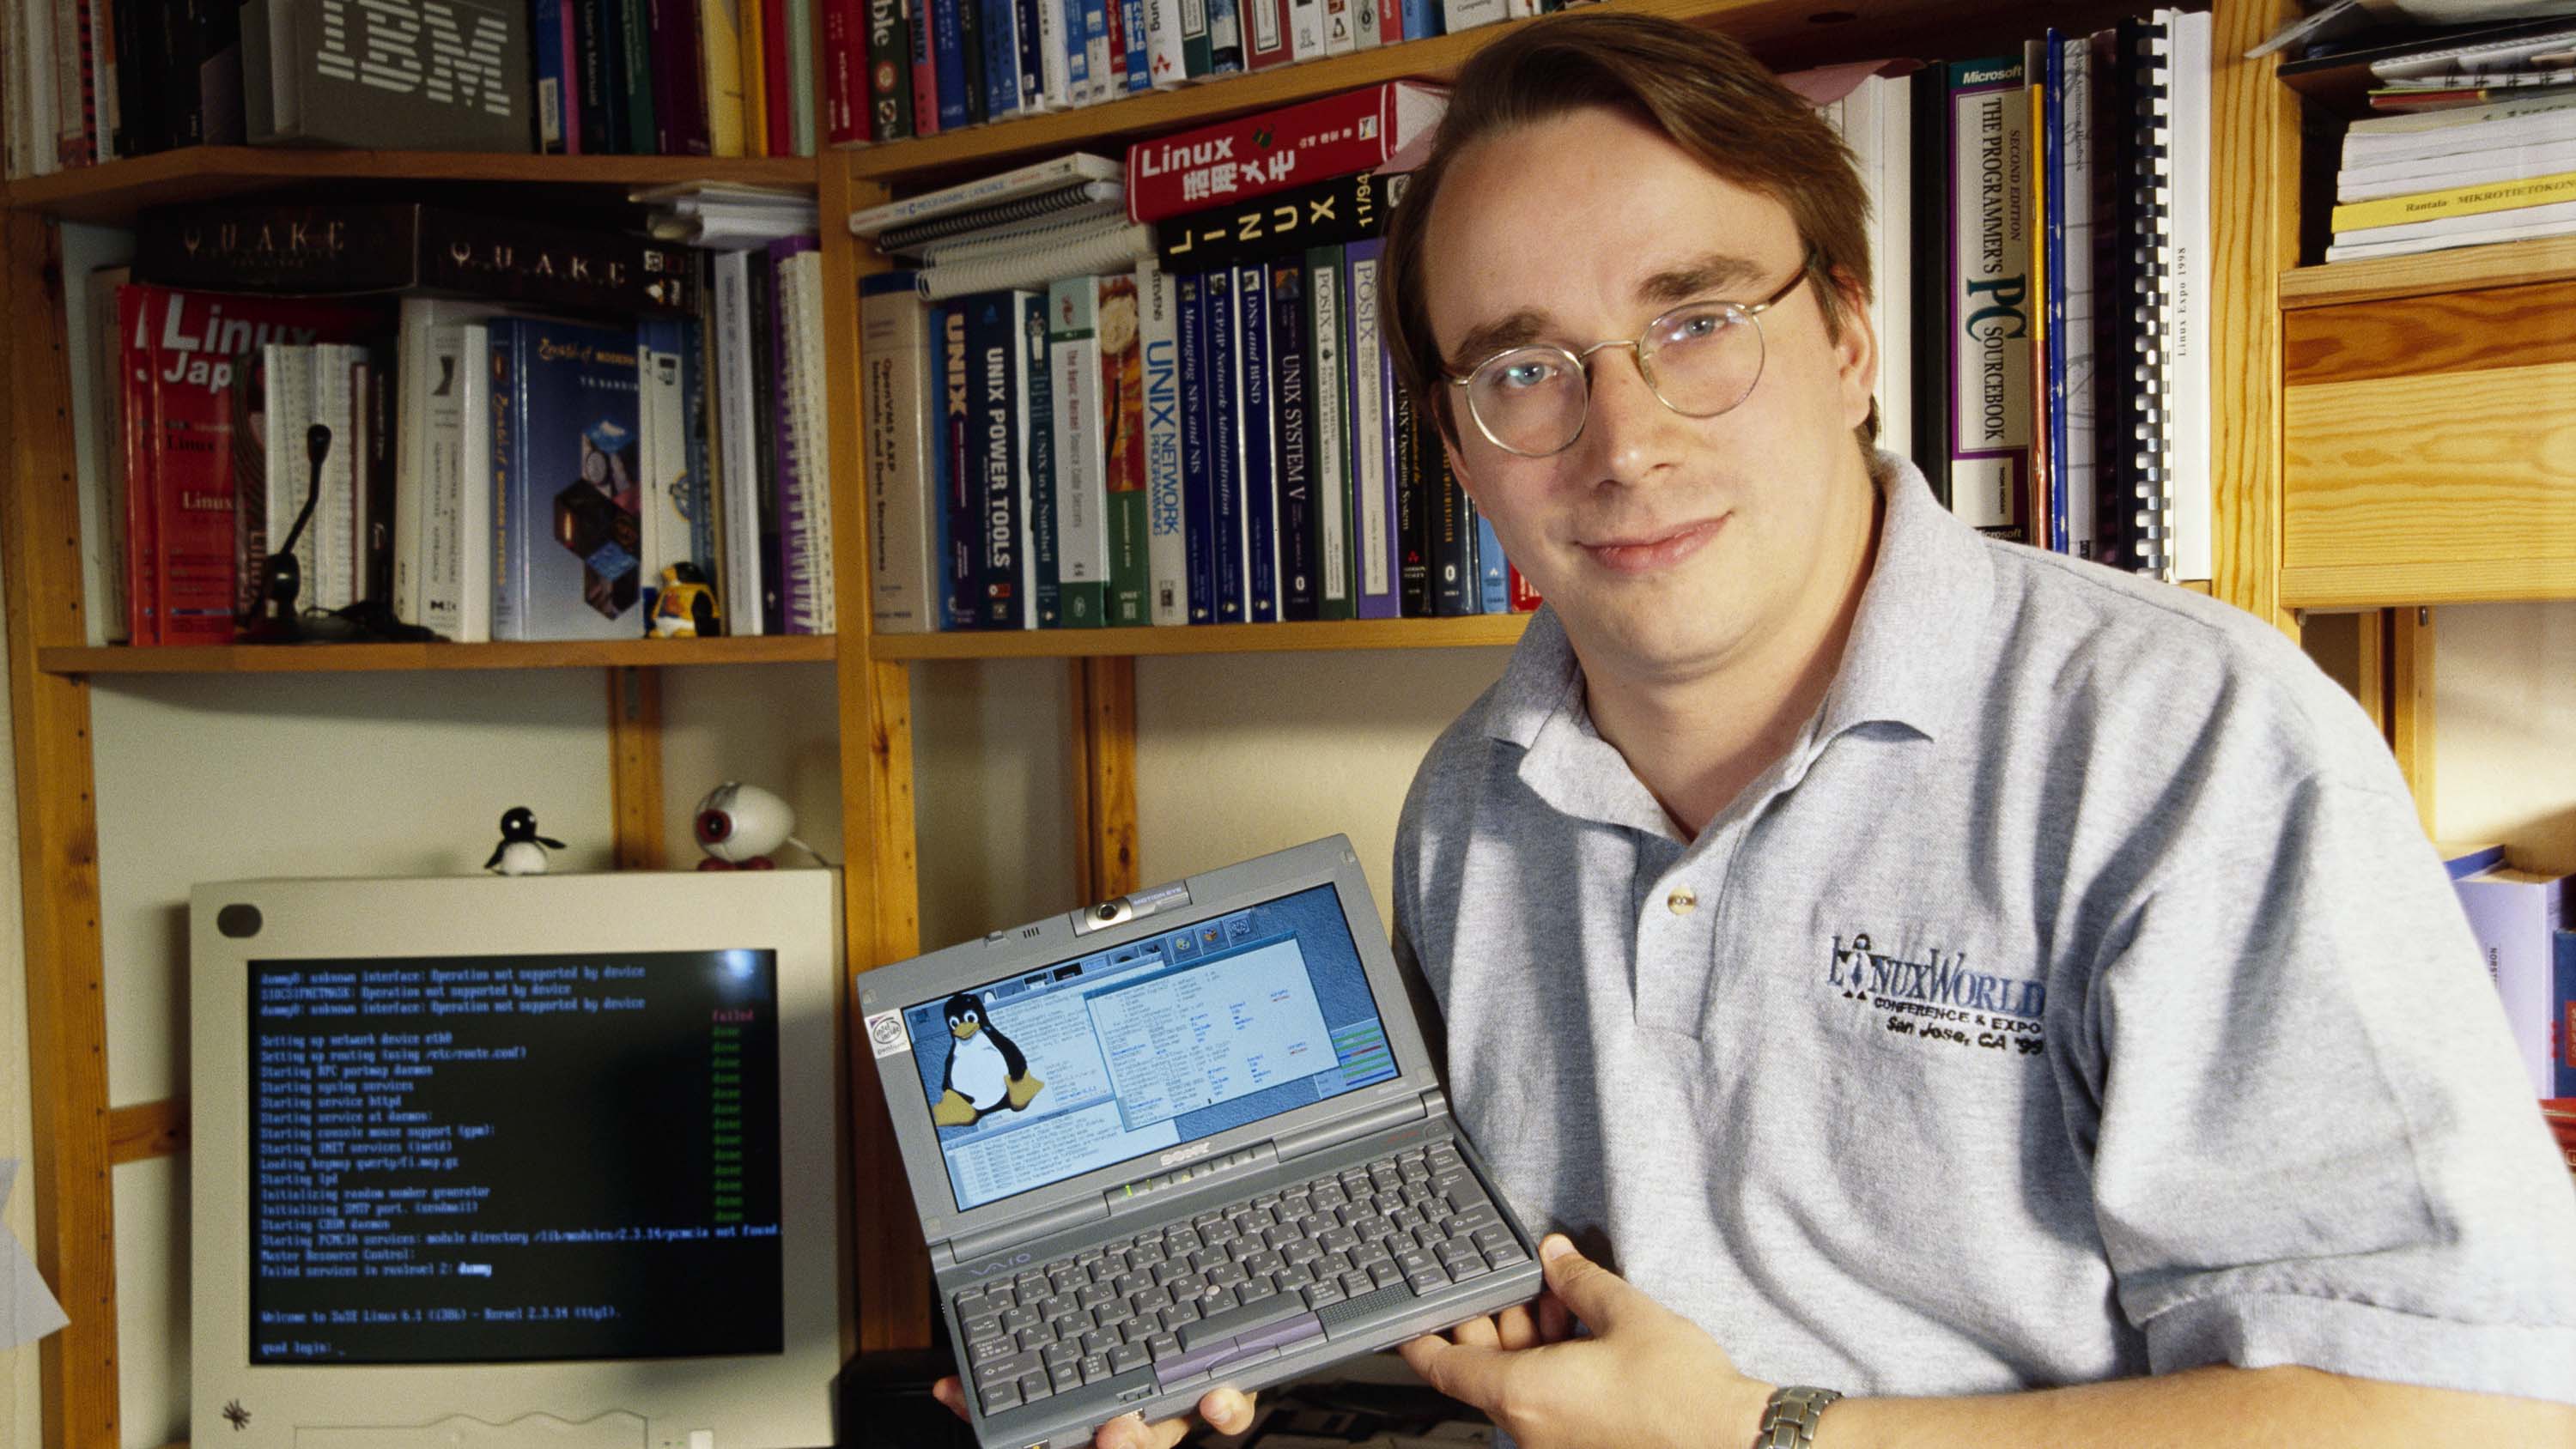
Torvalds emphasized that if a bug is identified by an AI tool, it is likely already known to others, rendering private security list reporting redundant and inefficient. He urged researchers to move beyond simple automated discovery, suggesting that if they intend to provide value, they should pair their findings with actual patches and a deeper understanding of the code.
This sentiment echoes broader concerns within the developer community regarding the quality of automated submissions. Jarom Brown, a senior product security engineer at GitHub, noted that while they welcome AI-assisted reports, volume does not equate to utility. Brown stressed that an unvalidated output lacks the impact of a verified, reproducible finding, encouraging researchers to prioritize depth over the sheer quantity of speculative reports to maintain their reputation and effectiveness.
Comments (0)
No comments yet. Be the first!